
Throughout the final month, intelligence companies, President Joe Biden, and huge firms like Google have all issued the identical warning — sounding alarms on the rising menace of cyber assaults coming from international governments.
"The largest menace we face as a rustic from a counterintelligence perspective is from the Folks's Republic of China, and particularly the Chinese language Communist Social gathering," Director of the Federal Bureau of Investigation Christopher Wray instructed 60 Minutes on Sunday.
"They're concentrating on our innovation, our commerce secrets and techniques, and our mental property on a scale that's unprecedented in historical past," he added.
In keeping with Google's Risk Evaluation Group (TAG), essentially the most malicious cyberattacks within the U.S. are coming from Iran, North Korea, Russia and China.
An official publish, written by Google safety engineer Billy Leonard, accused these nations of benefiting from public curiosity within the warfare in Ukraine to unfold malware.
"Authorities-backed actors from China, Iran, North Korea, and Russia, in addition to numerous unattributed teams, have used numerous Ukraine war-related themes in an effort to get targets to open malicious emails or click on malicious hyperlinks," Leonard wrote.
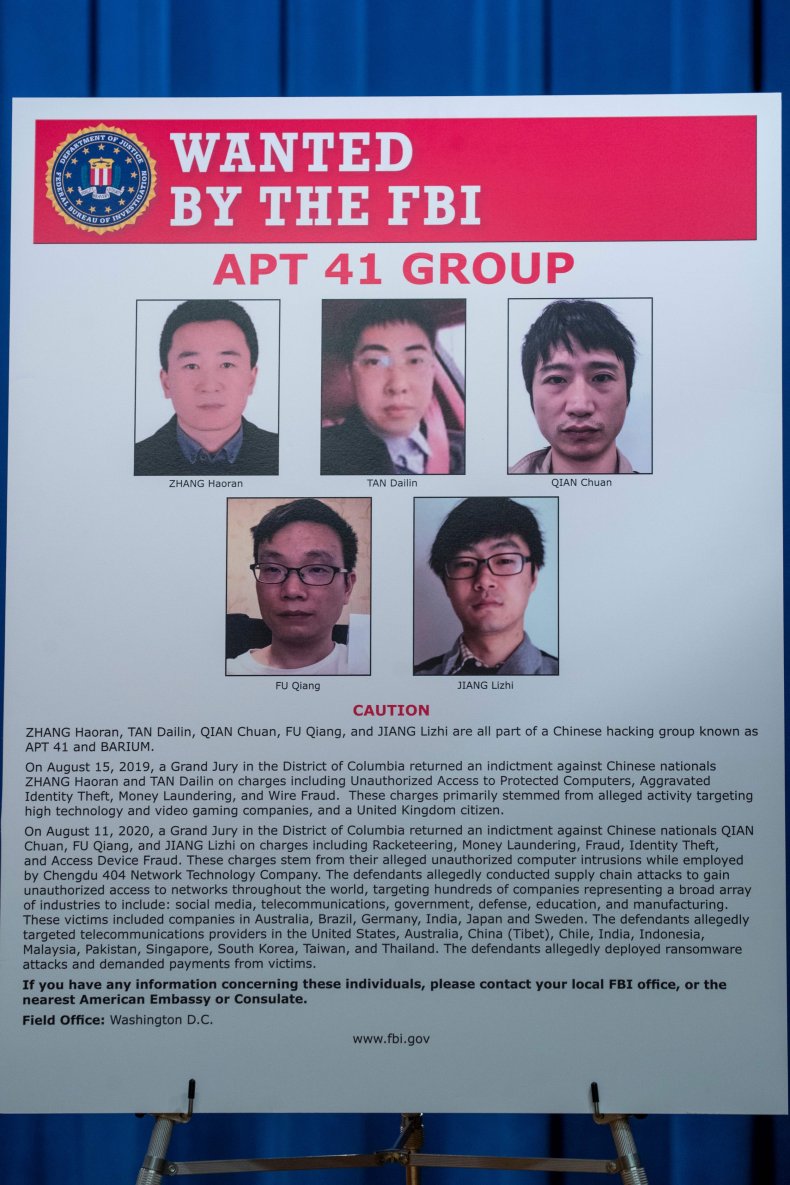
Final month, the Workplace of the Director of Nationwide Intelligence printed its 2022 Annual Risk Evaluation of the U.S. Intelligence Group. The report offers particular particulars on the threats every of those nations poses to home cybersecurity.
Whereas cyber-attacks from Iran are primarily retaliatory or focused towards Israel, a U.S. ally, assaults coming from Russia are actively geared toward disabling crucial infrastructure and manipulating communications organizations, in response to the report.
North Korea principally depends on espionage and cybercrimes, and is "well-positioned to conduct shock cyber-attacks given its stealth and historical past of daring motion," the report acknowledged.
However essentially the most alarming warning was issued about China.
The report calls China "the broadest, most lively, and protracted cyber-espionage menace to U.S. Authorities and personal sector networks," and argues that it's "virtually actually able to launching cyber-attacks that will disrupt crucial infrastructure providers inside the USA."
These experiences have alarmed policymakers, who've responded with commitments to spend money on a stronger, extra resilient nationwide infrastructure.
"We should work now to remodel the USA into essentially the most cyber-secure nation on the earth," wrote Republican John Katko, rating member of the Home Committee on Homeland Safety, in a current op-ed.
The home cybersecurity sector has seen speedy development since President Biden first took workplace, with revenues totaling about $40.70 billion in 2018 leaping to almost $58.65 billion in 2022, in response to Statista, which initiatives that home revenues will improve to at the very least $78.30 billion by 2026.
A good portion of this development is predicted to come back by means of private-public contracts, with Biden's most up-to-date price range plan requesting $10.9 billion in cybersecurity funding throughout civilian authorities companies.
"From day one, my Administration has labored to strengthen our nationwide cyber defenses," President Biden stated in an announcement on March 21, "mandating in depth cybersecurity measures for the Federal Authorities... and creating modern public-private partnerships and initiatives to boost cybersecurity throughout all our crucial infrastructure."
Business officers spoke in assist of the federal government initiative.
"Robust public-private collaboration is essential to proactively stopping or mitigating threat for the forms of vital nationwide cyber incidents we've seen proliferate over the past a number of years," Ryan Gillis, vice chairman of Cybersecurity, Technique, and International Coverage from Palo Alto Networks, instructed Newsweek.
Palo Alto, one of many largest firms within the cybersecurity sector, introduced a partnership with the White Home earlier this 12 months, during which they may collaborate to implement the Federal Zero Belief Technique, which requires companies to satisfy particular cybersecurity requirements by the tip of 2024.
The technique is predicted to drive federal authorities cybersecurity actions over the following two years and past, in response to Palo Alto's web site.
CrowdStrike, one other main cybersecurity firm, introduced an analogous partnership in December with the Cybersecurity and Infrastructure Safety Company (CISA).
CISA chosen the corporate to be a founding companion of its Joint Cyber Protection Collaborative, a bunch designed to guide the event of cyber protection operations plans for federal, non-public, and state authorities stakeholders.
Adam Meyers, CrowdStrike's senior vice chairman of intelligence, stated partnerships like these shall be important going ahead with the intention to make sure the resiliency of home cybersecurity infrastructure.
"Numerous organizations haven't but invested in cybersecurity," Meyers instructed Newsweek, "however they should with the intention to shield themselves, shield their clients, and shield their knowledge."
"Counting on antivirus that was constructed and conceptualized within the late '90s is not going to chop it with the menace actors that we're seeing at the moment," he added. "We have to have superior instruments."
Post a Comment